While other platforms prioritize, Moonfort has already fixed the vulnerability.
Beyond remediation. One message activates a fleet of agents that closes the full loop across your environment, deploying the fix, enforcing the guardrail, and preventing the next threat.
One fleet runs all 6 stages, so the work stops changing hands.
Surface, investigate, remediate, prevent, enforce, and guide, across your cloud, your pipelines, and your identities, through the control planes you already own.
One workforce. No silos.
Silos are where ChaseOps thrives. Engineering, SecOps, vulnerability management, threat intel, identity, each with its own tool, its own queue, its own blind spots. Resolving a single finding bounces across three teams before anything in the environment changes. Moonfort is the one workforce operating across all of them, in every estate.
Financial Services
Your backlog gets planned around, not cleared. Closing one finding still travels through the SOC, vulnerability management and the cloud team before anything in the environment changes. One workforce closes it end to end. The fleet works that backlog against your own architecture, revokes the identity path into the cardholder data environment that the application has never called on your approval, and an SCP stops the next role being created with that reach. DORA rewards exactly this, remediation you can prove on demand, and the evidence arrives attached to the change.
Telecommunications
Accounts, subscriptions and projects come online faster than any team can review them, and your scanners already return more than you could ever clear. Every new environment is in scope the day it ships. The fleet works the backlog down to the set that is genuinely reachable, closes each one through the estate's own controls, and runs the whole loop on every new GCP project the day it appears, so coverage keeps pace with an estate that grows every week.
Manufacturing and Automotive
Telematics, OTA and charging backends grew faster than your security engineering could, so an outside firm runs the cloud security and the knowledge leaves when the engagement ends. Here the expertise arrives as software, and stays. The fleet does that engineering inside your own accounts and pipelines, closes the reachable exposures, and writes the guardrails in Terraform so the misconfiguration is caught on the pull request. UNECE R155 asks for a security management system you can keep proving, and these controls stay current as the estate changes.
Technology and SaaS
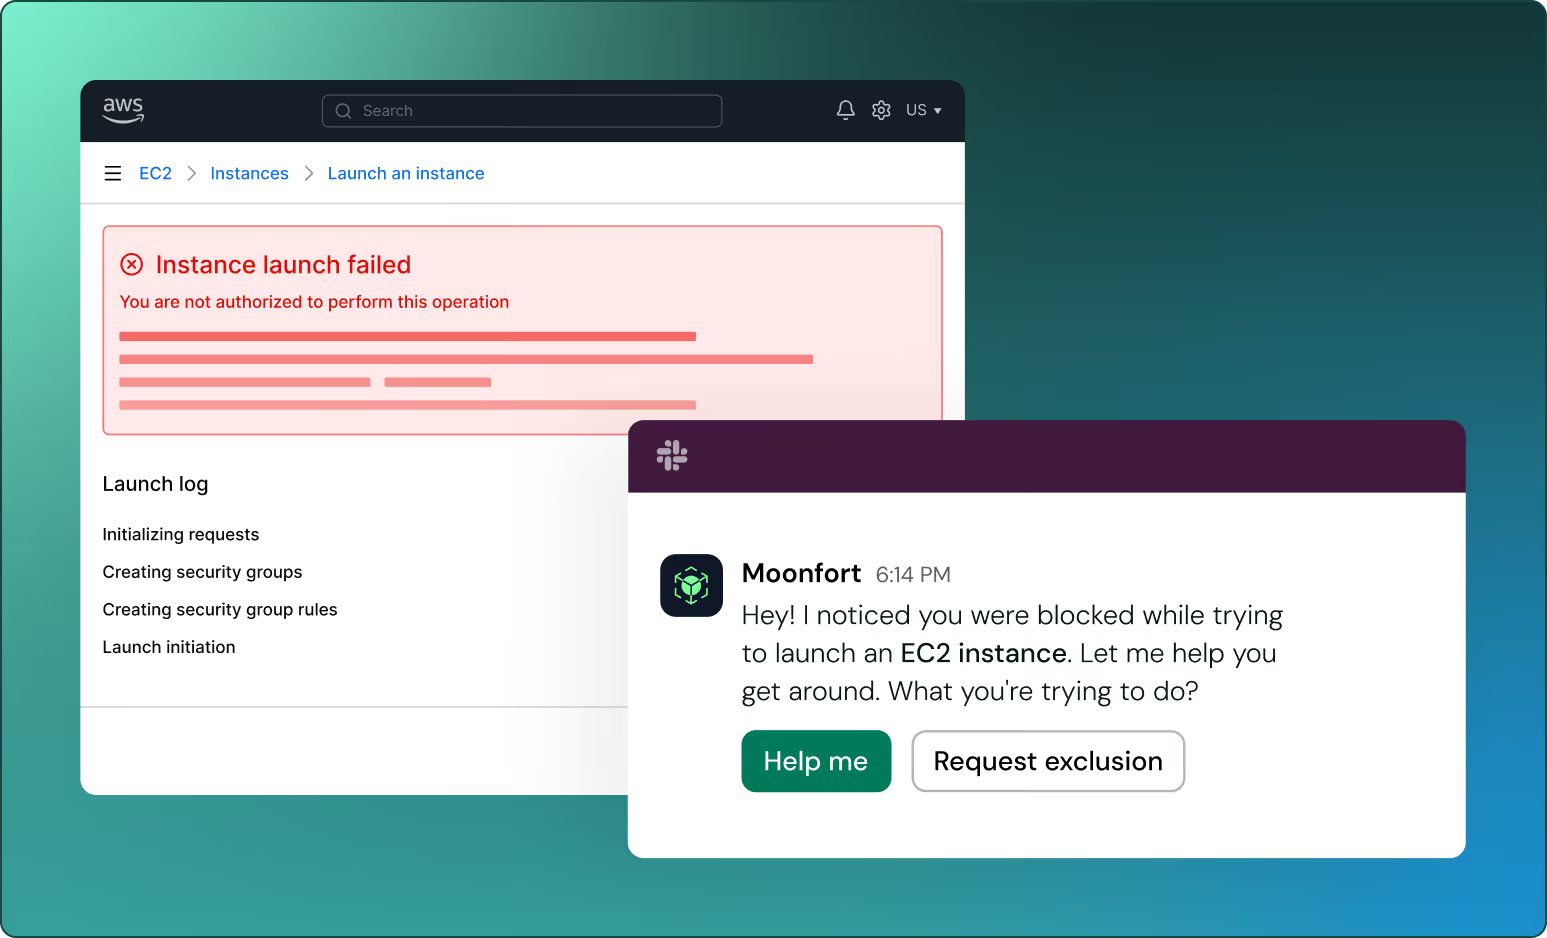
A guardrail blocks an engineer mid-deploy. Instead of a ticket, they get a message in Slack asking what they were building, and a secure route to the same outcome. The fleet reads your Jira and Confluence to learn how your teams actually ship, returns a secure route to the same outcome, and the control holds because there is now a way through it. You ship faster than you can hire the senior engineers to keep up, and this is how security keeps pace instead of throttling the release.
Aviation and Transportation
Booking, loyalty and data platforms sprawl across a corporate cloud that only grows, while security-engineering headcount stays flat. Capacity, not headcount. The fleet scores that backlog against your own architecture, closes what is genuinely reachable through your own control planes, and holds it with a guardrail in each account. A thin team covers a surface it could never have staffed for.
Healthcare
Your backlog competes with clinical priorities for the same scarce engineers, and every change to a regulated estate has to be provable. Every action carries its evidence. The fleet reads an account's grants against its actual use, revokes the path into the ePHI store it has never called on your approval, and keeps the non-usage evidence attached to the change. Remediation and the record become the same act, with a sign-off on every one.
One fleet. The full security cycle.
Beyond remediation. Moonfort finds the gap, fixes the vulnerability, enforces the guardrail, and prevents the next threat.
Surface Gaps
Everything you run
Continuously scans your environment and brings findings from your existing security tools into one place.
- Connects to your cloud accounts, pipelines, and repositories
- Ingests from the scanners you already own
- Resolves each asset to what it can reach and the identity attached to it
- Re-scans on change, so new infrastructure is in scope the day it ships
Investigate Risks
Signal from the noise
Investigates every finding to determine what matters, why it exists, who owns it, and what fixing it could affect.
- Proves the vulnerable path is reachable and executes, read-only
- Establishes blast radius from the identity attached to the asset
- Confirms the finding against runtime logs and application source
- Identifies the owner and opens the ticket to them
Fix Issues
Fixed end to end
Determines the root cause, builds the remediation, analyzes its production impact, and carries the fix through the approved workflow.
- Produces the artefact: the WAF rule, the IAM policy, the SCP, the Terraform
- Checks production impact against runtime behaviour before proposing
- Opens the pull request and the ticket with reasoning and evidence attached
- Deploys on your green light, or hands you the change to apply
Prevent Attacks
Stopped in real time
Deploys real-time prevention controls while the permanent remediation is underway.
- Denies anonymising VPN sources, reconnaissance, and secrets enumeration
- Contains the session on cross-role assumption outside the normal pattern
- Built on how threat actors operate, from years of incident response
- Scoped to one proven exposure, so the control stays narrow and reversible
Enforce Guardrails
Guardrails everywhere
Turns what it learns into controls enforced across cloud environments and CI/CD pipelines.
- Converts a closed finding into a guardrail that blocks the class at source
- Enforces the same rule across every account and every pipeline
- Runs in audit before it blocks, so you see the impact first
- Writes in your own policy artefacts: SCPs, RCPs, IAM boundaries
Guide Teams
Secure and fast
Works directly with developers, IT, DevOps, and platform engineers through Slack or Teams when a control blocks their work.
- Opens a Slack or Teams thread within seconds of the block
- Reads your Confluence and Jira, so the alternative fits your stack
- Returns the working steps, so the engineer ships the same day
One fleet takes security from thousands of findings to lasting prevention. It investigates every issue, fixes what matters, protects the environment while the fix is underway, enforces the lesson everywhere, and guides teams forward.
Your entire security fleet, one message away.
Security engineers work with Moonfort directly in Slack or Teams. Ask for evidence, investigate a risk, approve a fix, or enforce a guardrail. The fleet carries the context and executes the work.
Hit Reset
The fleet works down the backlog your scanners already produced. Each reachable finding is closed end to end, with the owner on the ticket, so the pile that never shrinks finally does.
Draw Boundaries
You set the red lines. The fleet writes them into your own SCPs, IAM policies, and pipeline checks, so the same guardrail holds in every account.
Stop New Noise
With the guardrails live, the misconfigurations behind the alerts stop being created, and the next one is caught on the pull request before it reaches production.
You message Moonfort when you need it. Moonfort messages you when it needs a decision.
Security execution and knowledge are fragmented across tools, teams, and individuals.
When a risk spans tools and teams, context must be rebuilt, priorities revisited, and the response manually coordinated. As the environment grows, so does this operational burden.
Security execution and knowledge are fragmented across tools, teams, and individuals.
When a risk spans tools and teams, context must be rebuilt, priorities revisited, and the response manually coordinated. As the environment grows, so does this operational burden.
What cybersecurity leaders ask before they move.
- Is Moonfort an AI assistant?+
Moonfort is an agentic security workforce. An assistant helps a security engineer analyze information. Moonfort’s specialized agents investigate issues, determine root causes, build fixes, enforce controls, and surface decisions with supporting evidence. The security engineer sets the boundaries and remains in control.
- Is Moonfort an autonomous SOC?+
Moonfort goes beyond traditional SOC workflows, but its deepest capabilities today are in cloud security engineering, vulnerability management, and exposure management. It also supports selected alert-triage and threat-intelligence use cases. Broader phishing, endpoint investigation, and containment capabilities are being developed.
- Does Moonfort replace our existing security tools?+
Moonfort can scan your environment directly and connect to findings from existing CSPM, CNAPP, and other security platforms. It turns those findings into investigations, decisions, fixes, and preventive controls.
- Can Moonfort make changes to production?+
Only within the boundaries your team defines. Moonfort can generate the required code and configuration, including pull requests, JSON policies, IAM changes, SCPs, and WAF rules. Your team can approve direct execution, review each proposed action, or keep Moonfort read-only and implement the changes manually.
- How do security engineers stay in control?+
Security engineers define permissions, approval requirements, and operational boundaries. Before an action is taken, Moonfort can provide its reasoning, supporting evidence, root-cause analysis, and expected production impact.
- How do we interact with Moonfort?+
Security engineers work with Moonfort through Slack, Microsoft Teams, or its interface. They can request evidence, investigate a risk, review impact, approve a fix, build a control, or ask why an action was recommended. Moonfort can also initiate the conversation when a decision is required.
- How does Moonfort prevent the next issue?+
Moonfort turns what it learns from existing risks into preventive controls across cloud environments and CI/CD pipelines. While a permanent remediation is underway, it can also deploy controls against exploitation and post-exploitation activity.
- Does Moonfort replace security engineers?+
No. Security engineers provide strategy, judgment, permissions, and boundaries. The agents perform the investigation, remediation, enforcement, and other operational work, allowing each engineer to direct significantly more security execution.
- What happens when a security control blocks an engineer?+
Moonfort can contact the affected developer, IT, DevOps, or platform engineer in Slack or Teams, explain the block, and provide a secure alternative based on the organization’s environment and controls.
- Where does Moonfort operate?+
Moonfort is cloud-first, with current work centered on AWS, Azure, and GCP. Its coverage is expanding into on-premises, SaaS, and hybrid environments.
One message, and your Moonfort fleet is already completing the full security cycle.
Your limitless security team is here.